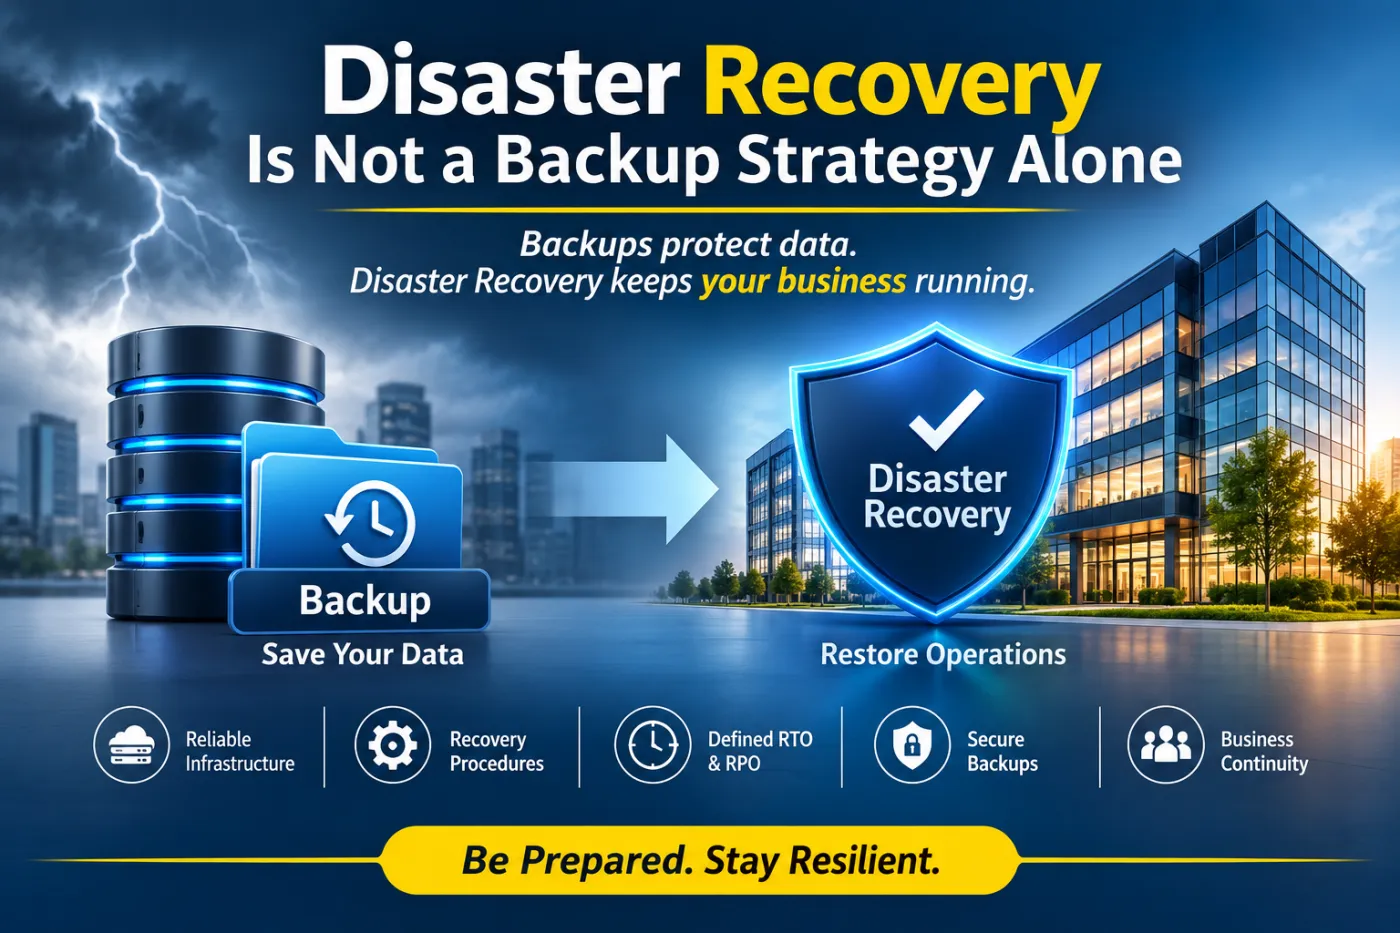
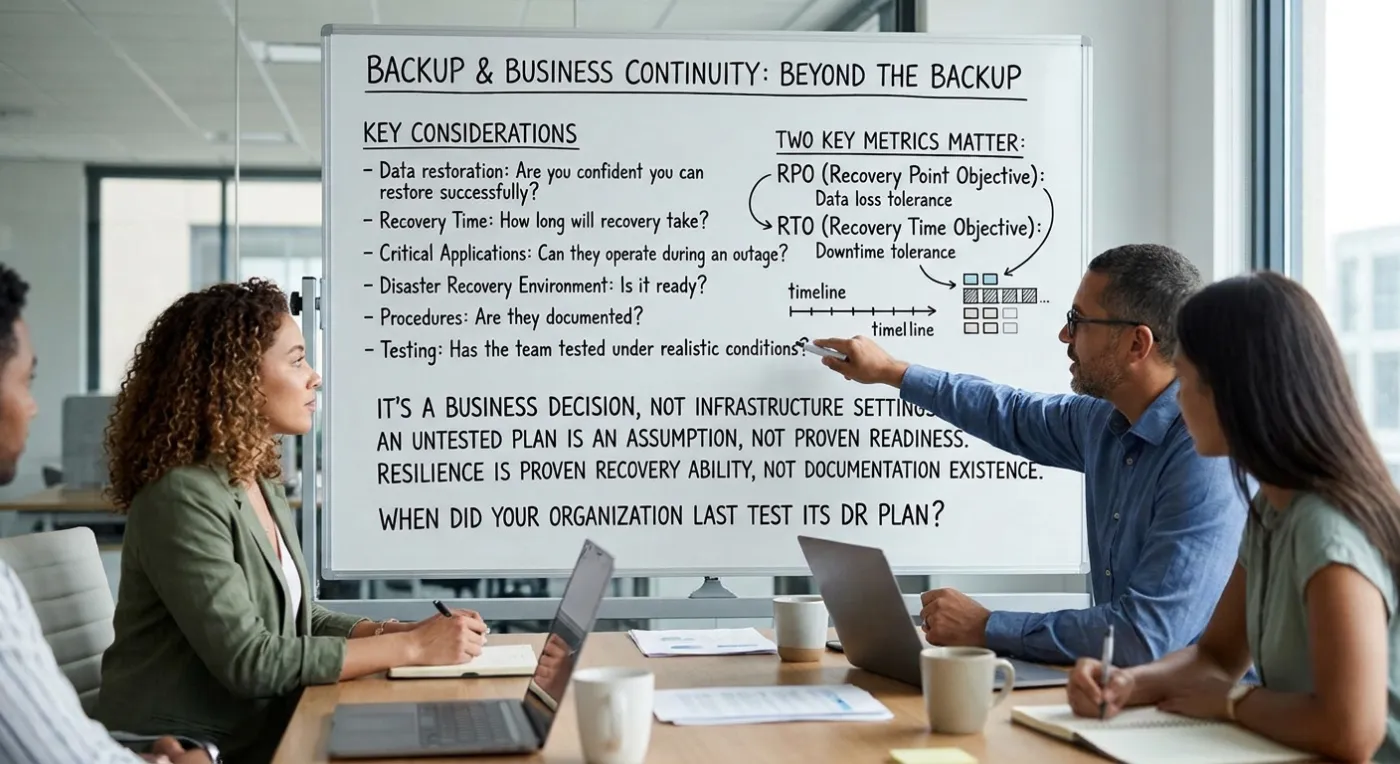
Disaster recovery is more than maintaining regular data backups. It is about ensuring that critical systems, applications, infrastructure, and business operations can be restored within acceptable timeframes when unexpected disruptions occur. A resilient organization prepares not just to protect its data, but to keep its business running.
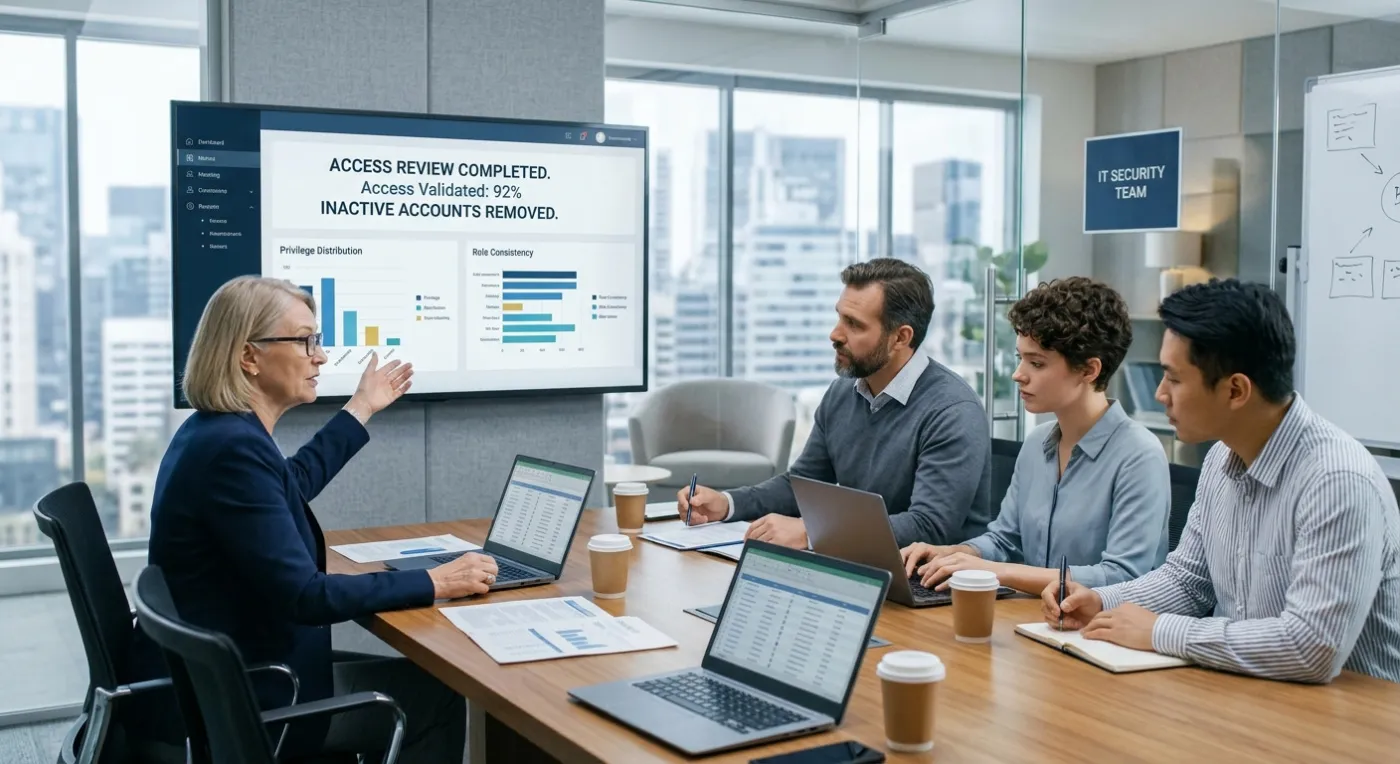
Many organisations invest heavily in advanced cybersecurity tools, yet they frequently overlook one of the simplest security controls: regular access reviews. Over time, as employees shift roles and external contractors conclude their work, unmonitored privileges accumulate, leaving dormant or excessive permissions open. Technology and identity management systems alone cannot mitigate this risk; proactive governance is essential to constantly evaluate not just who holds access, but whether that access remains appropriate.
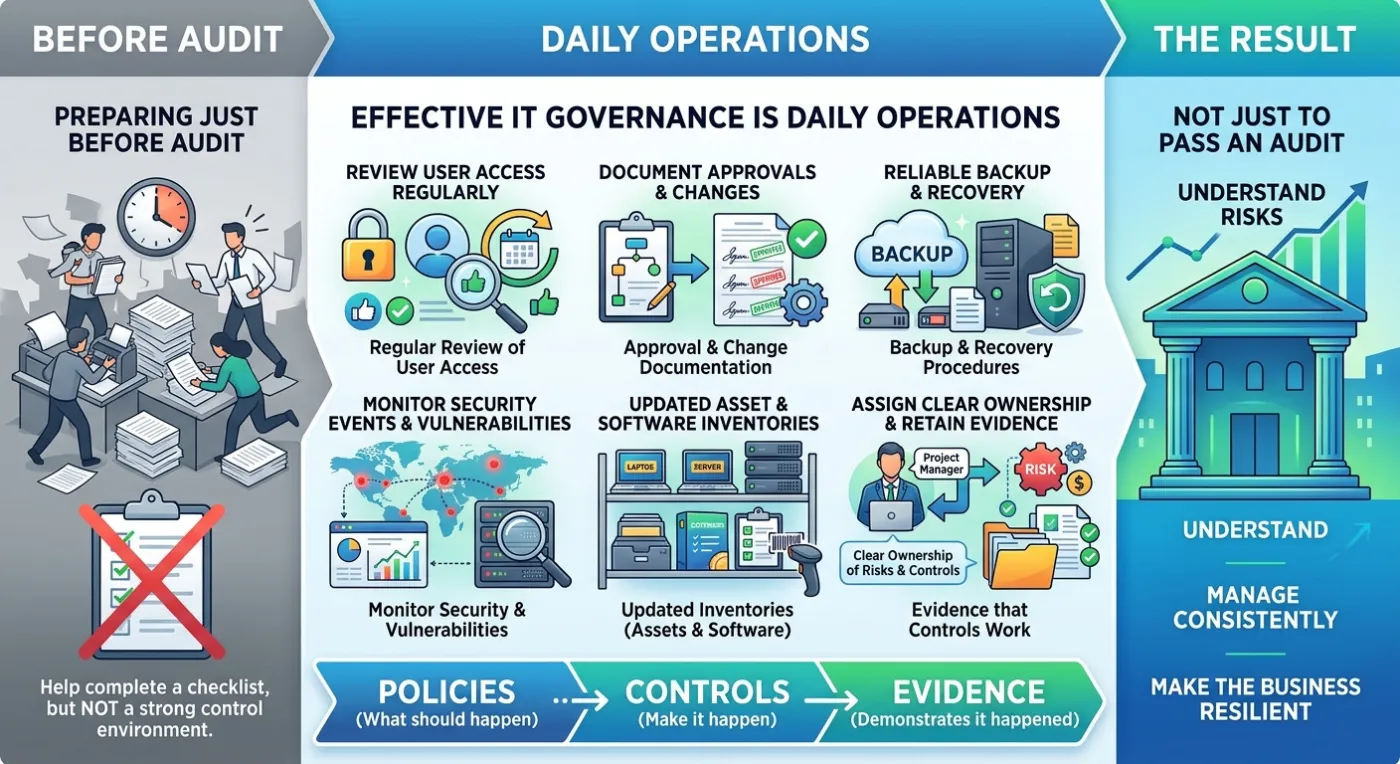
Effective IT governance is woven into the fabric of daily operations rather than assembled in a frantic scramble right before an audit. True control environments are built through consistent practices—such as regular user access reviews, meticulous approval documentation, reliable backup procedures, and clear risk ownership—transforming governance from a compliance checklist into an engine for operational resilience.
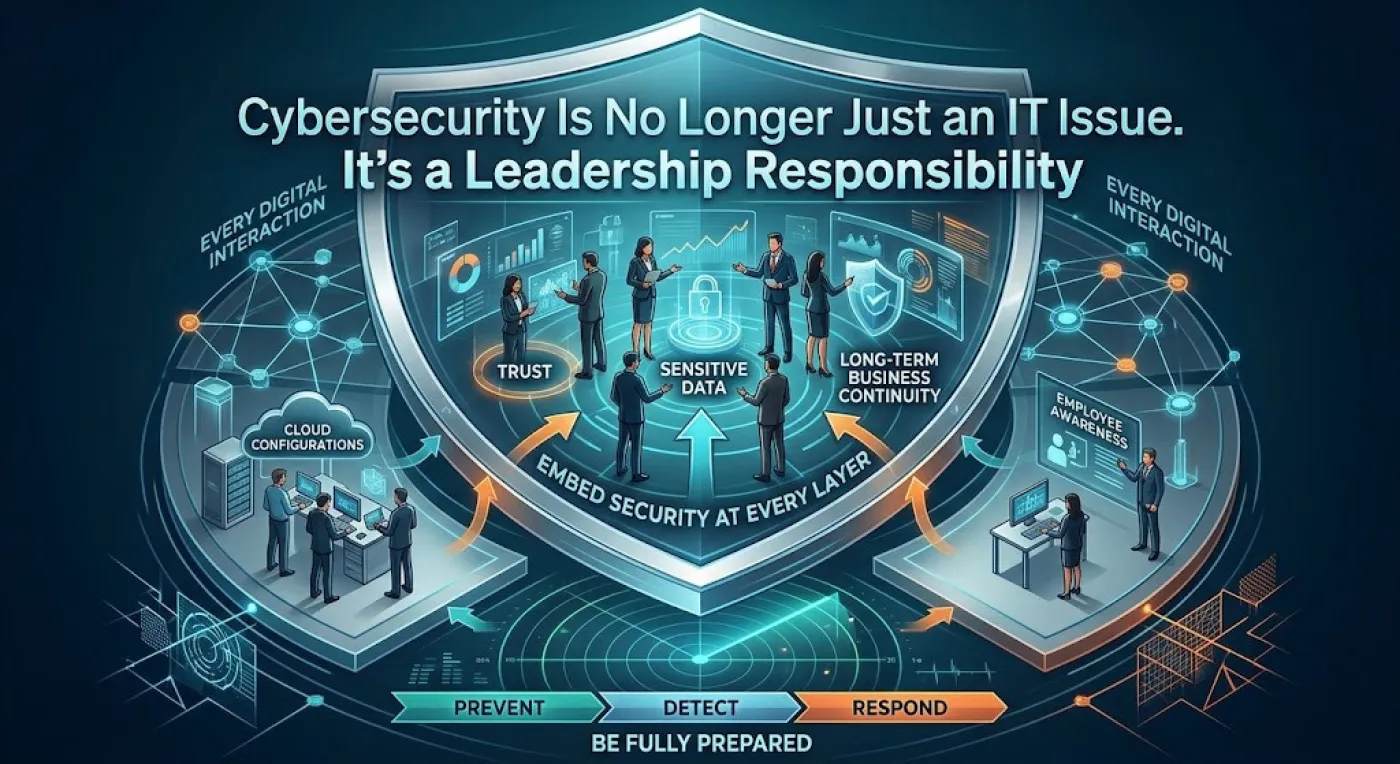
For modern organizations, cybersecurity is no longer just about keeping systems operational—it is about protecting trust, sensitive data, and long-term business continuity. Because every digital interaction introduces potential privacy risks, enterprises must embed security into every layer of their operations, from cloud configurations to employee awareness. The fundamental challenge for IT leaders is not predicting if a cyber threat will occur, but ensuring the organization is fully prepared to prevent, detect, and respond when it does.
Business continuity demands far more than routine backups; it requires a validated strategy for total operational resilience. Backups preserve data, but disaster recovery depends on your ability to restore systems and keep critical applications running during an outage. This relies on defining two key business metrics: Recovery Point Objective (RPO), which measures tolerable data loss, and Recovery Time Objective (RTO), which limits acceptable downtime. An untested plan is just an assumption. Resilience is measured not by documented procedures, but by proven recovery capabilities.
Speed without stewardship is a liability. While artificial intelligence dramatically accelerates output in software development and IT operations, it cannot shoulder the burden of accountability. For IT leaders, the true competitive advantage today isn't widespread adoption—it's strategic restraint. By pairing AI-driven velocity with rigorous human validation, security checks, and clear ownership, organizations can turn raw efficiency into sustainable value.